Skip to content

Call +1 (888) 896-7580 for Proactive Cyber Security© Services and Solutions

January 18, 2015January 31, 2015 by Michael Peters
Bookmark

2015 Audit Anarchy Infographic

There is a huge difference in the very traditional methodology used by almost all audit firms and the proactive constant auditing methodology used by Lazarus Alliance. This infographic explains those differences along with shining a little light on some dirty techniques used by the big expensive bully firms.
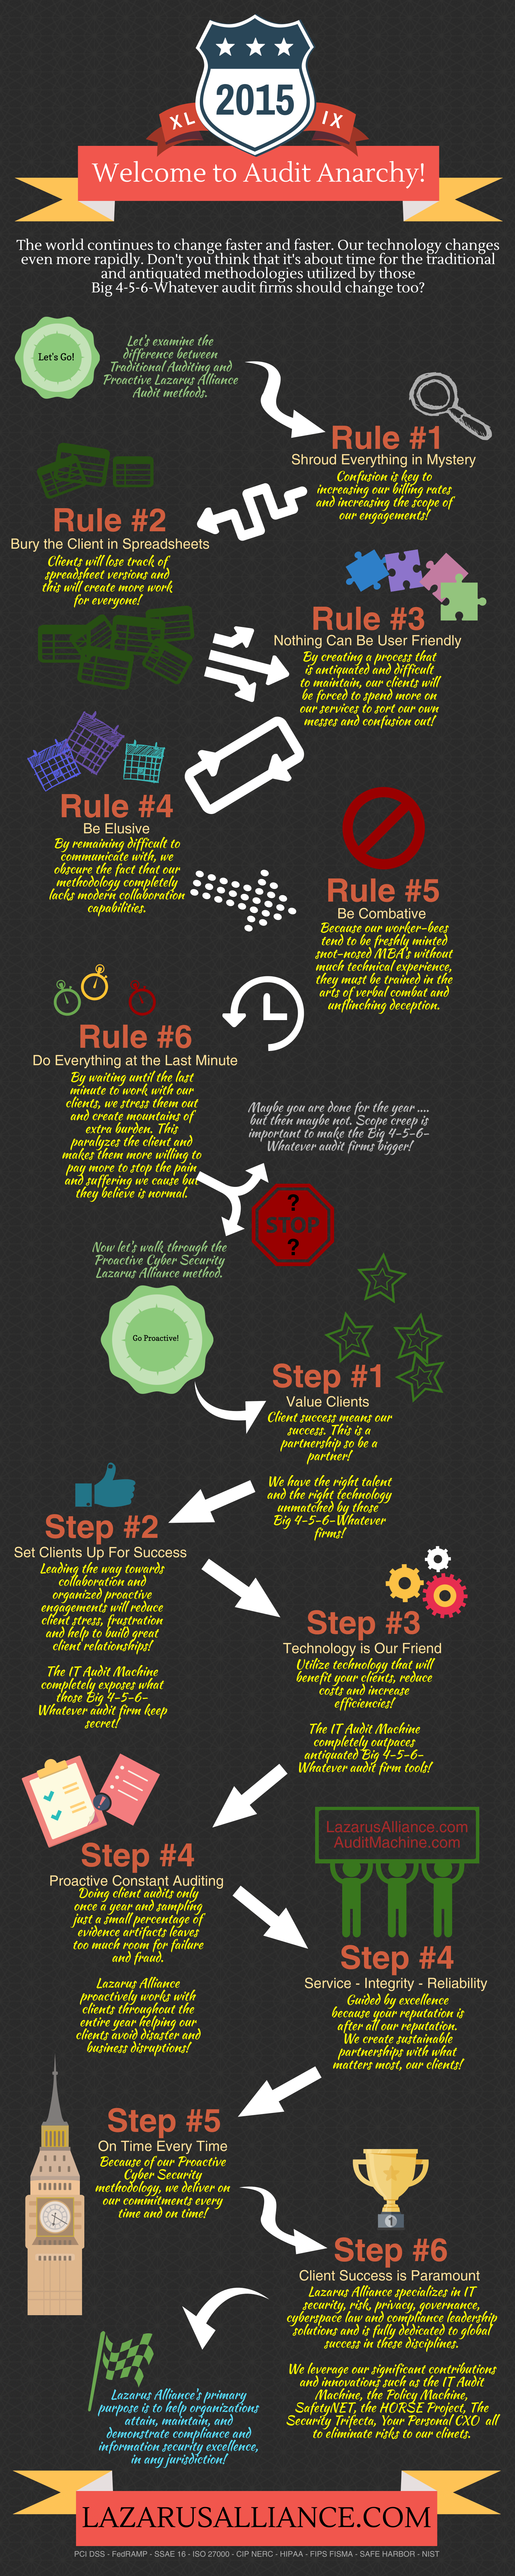
2015 Audit Anarchy Model


CXO, HORSE Project V1, Lazarus Alliance, The Security Trifecta, Your Personal CISO

Post navigation

← Cyber Security Comes In Only Two Flavors
Demise of the Mighty Merchant: rampant credit card fraud and what to do about it. →

Looking for Something?

Recent Updates

  • 7 AI Automation Tactics for GRC Compliance by Continuum GRC
  • NIST 800-171 Rev 3 Adoption: Risk Management Strategies
  • FedRAMP Class B & C Intake Is Now Live | FedRAMP 20x 3PAO
  • ISO 27001 2026 Transitions: Continuum GRC Risk Management
  • ISO 42001 AI Certification: 5 Key Governance Strategies
  • CMMC 2.0 Audit Readiness: Lazarus Alliance Compliance Assessments
  • ISO 27001 Updates: Continuum GRC Governance and Compliance Audits
  • HIPAA OCR Enforcement: Lazarus Alliance Risk Management
  • ISO 27001 Transition: Continuum GRC Cybersecurity Audits
  • ISO 27001:2022 Transition Audits by Lazarus Alliance Experts

Site Administration

  • Log in
  • Entries feed
  • Comments feed
  • WordPress.org